

Imprivata ID analysis by Appwee
In a hospital or clinic, signing in is rarely an isolated task. A clinician may move between a workstation, a shared computer, a medication area, and a mobile device while trying to keep attention on a patient. That is the setting where Imprivata ID makes sense. It is a free medical authentication app from Imprivata, Inc, built to support a more secure sign-in process for healthcare professionals rather than to act as a general-purpose password manager.
I approached it as a workflow tool, not as an app I would open casually every day. Its value depends heavily on how an organization has configured its clinical systems, but the basic idea is easy to understand: the app becomes part of the identity check required before accessing protected healthcare resources. When that process is arranged well, it can reduce interruptions. When the surrounding system is poorly prepared, the app can feel like one more step added to an already busy shift.
Following a clinical sign-in from start to finish
The starting condition: access is needed quickly, but security still matters
Imagine a nurse beginning a shift and needing to use a shared workstation. The computer may already be in a clinical area, but access still has to be tied to the correct person. A simple password can be awkward in this situation: it has to be remembered, entered accurately, and protected from people nearby. Reusing a password across systems would create an even bigger problem, especially in a medical environment.
Imprivata ID is designed for the point where identity and speed meet. The app does not replace the hospital’s wider access controls; instead, it serves as a mobile part of the authentication workflow. That distinction is important. Someone downloading it independently should not expect it to unlock ordinary phone apps, websites, or personal accounts. Its usefulness comes from being connected to an organization’s approved Imprivata setup.
That makes the intended audience quite narrow, but also quite clear. I would consider it for medical professionals whose employer already uses compatible Imprivata authentication services. I would not recommend installing it simply because the name sounds relevant to healthcare. Without the matching workplace configuration, there may be little practical value in keeping it on a personal phone.
Step one: preparing the phone before the shift
The first meaningful part of the experience is not the sign-in itself. It is getting the phone ready to participate in the organization’s authentication process. In a real workplace, that usually means following instructions from an IT or security team and completing whatever enrollment process the employer requires. The app is not something I would treat as a standalone setup with a universal path for every user.
This is one of the first trade-offs. A consumer app can often be installed, opened, and understood within minutes. A clinical authentication tool has to fit an employer’s identity rules, so the setup is more dependent on the institution. That dependency may feel inconvenient, but it is also part of why a healthcare organization would choose a dedicated solution rather than ask staff to improvise with personal password tools.
Before relying on it during a busy shift, I would test the complete route with the organization’s support team. The useful test is not merely whether the app opens. It is whether the phone, the user account, and the target clinical workstation all recognize one another at the moment access is needed. This is a practical tip that is easy to overlook: authentication apps should be checked at the actual point of work, not only from a quiet office.
Step two: responding when a workstation requests verification
Once the account is enrolled and the clinical environment is configured, the workflow becomes more purposeful. A clinician reaches a workstation or protected service, enters the information requested by the organization, and then uses the mobile app as part of the verification step. The exact screen sequence can vary with the employer’s setup, so I would avoid assuming that every hospital presents the same prompts.
The important experience is the handoff between the shared computer and the phone. The workstation begins the access request, while the phone confirms that the person attempting to continue has access to the enrolled authentication device. In a well-designed routine, this can be quicker and less exposed than typing a long password where other people may be working nearby.
That does not mean the phone disappears from the process. I still have to keep it available, charged, and usable. A device locked in a bag, left in a charging area, or affected by a change of phone can turn a supposedly quick sign-in into a support issue. For staff who regularly move between locations, this physical dependency is worth considering before calling the workflow seamless.
Step three: completing the handoff without losing the clinical task
The strongest part of the concept is the handoff itself. A clinician can begin at the computer, use the phone for the identity confirmation, and return to the clinical screen without sharing credentials with a colleague. That separation is useful in environments where several people use the same equipment across a shift.
I also see a less obvious benefit in role changes. If one professional finishes with a workstation and another takes over, a personal authentication step helps keep the transition connected to the right user instead of leaving the previous person’s session informally available. The app cannot solve every session-management problem, but it supports a more disciplined habit: each person authenticates as themselves rather than treating a shared computer as a shared identity.
There is a human factor here too. Staff need to understand what the prompt means and when it is safe to approve or complete it. In any authentication workflow, blindly accepting a request is a weakness. Training should make clear that the phone action belongs to a sign-in the user has just initiated. If an unexpected request appears, the sensible response is to pause and contact the organization’s support channel rather than approve it automatically.
Step four: reaching the result
The desired result is not a new feature on the phone. It is access to the clinical workstation or service with less reliance on exposed, repeatedly typed credentials. When the workflow succeeds, the app has done its job quietly. The clinician can return attention to charting, reviewing information, or continuing patient care.
That quietness is a strength. Imprivata ID is not trying to entertain me, organize my personal life, or replace a broad productivity suite. Its purpose is narrow and operational. For the right organization, a focused tool is preferable to a collection of unrelated authentication methods that staff have to remember separately.
Still, I would judge the result by the full chain rather than the app alone. If the workstation is slow, the account is misconfigured, the phone has no usable connection, or the user has not been enrolled correctly, the final outcome will still be frustrating. The app participates in the result; it does not control every part of it.
Where the flow breaks in everyday use
The most realistic failure point is a mismatch between the user’s expectation and the organization’s setup. Someone may install the app and assume it will immediately provide access. In practice, a medical authentication app needs the employer’s systems, account policies, and support process around it. I would confirm workplace compatibility first, then install it, rather than doing the reverse.
Another weak point is device replacement. If a staff member changes phones, loses one, or restores a device from backup, authentication access may require attention from the organization. That is not a reason to dismiss the app, but it does mean the phone should be treated as part of a professional access workflow, not as an interchangeable accessory.
Battery and availability are also practical concerns. A phone-based check is only convenient when the phone is present and ready. Staff working long shifts should build a habit of starting with enough charge and knowing the approved route for a failed sign-in. The best authentication design still needs a fallback process for real-world interruptions.
How it compares with familiar alternatives
The usual alternative is password-only access. Passwords are familiar and do not require a second device, but they can be harder to use safely on shared clinical computers. They may also encourage shortcuts when staff are under pressure. Imprivata ID offers a different balance by making the phone part of the identity check, which can improve the workflow when the environment is configured for it.
Another alternative is a physical badge or token. A badge can be convenient for staff who already carry one, while a separate token avoids relying on a personal phone. On the other hand, physical items can be forgotten, damaged, or unavailable during a handoff. A phone-based approach may be more practical for some teams, but it introduces its own dependency on the mobile device.
General authentication apps can be a better fit for personal accounts or workplaces that use common online services. I would choose one of those when I need broad compatibility across unrelated services. Imprivata ID is more specialized: its advantage is not universal coverage, but its place inside a clinical access workflow supported by Imprivata’s platform.
What the app is like as an Android installation
As an Android app, it supports devices running Android 6.0 or later. That gives it a wide compatibility range for organizations with a mixture of older and newer phones. The current version is 2026.1.1.144, so users should pay attention to the version installed by their organization’s normal mobile-management process and avoid assuming that every device has the same release.
The app is free to install and carries an Everyone age rating. Those details make it easy to obtain from a personal perspective, but they should not be confused with unrestricted access. The download cost is not the main consideration here; the real question is whether an employer’s clinical environment supports it and whether the user can complete enrollment correctly.
Its public reception is mixed, with an average rating of 3.0 from around 509 ratings and 234 written reviews. I would read that as a reminder to keep expectations realistic. A rating cannot separate phone problems from workplace configuration problems, and authentication apps are especially dependent on systems outside the app itself. The app has reached over 500K installs, which indicates meaningful adoption, but adoption alone does not guarantee a smooth experience in every institution.
Who should use it, and who should skip it
I think it is a sensible choice for a clinician, contractor, or other medical professional whose organization explicitly tells them to use Imprivata ID. It is particularly relevant when staff share workstations, need a more controlled identity check, or move between clinical areas and want a consistent mobile step in the sign-in process.
I would skip it if I were looking for a personal password manager, a general two-factor app, or a way to secure unrelated consumer accounts. I would also avoid relying on it without first confirming the employer’s enrollment instructions. Installing it ahead of that conversation can create confusion, especially if the organization has a specific support path for activation, phone changes, or access problems.
Managers and IT teams should judge it slightly differently from individual users. For them, the question is whether the complete handoff is understandable under pressure. A technically secure process that staff cannot follow during a busy shift will create workarounds. Before wider adoption, I would observe a real transition between users, check how a replacement phone is handled, and make sure staff know what to do when the app or workstation does not complete the request.
Small habits that make the workflow more dependable
My first practical recommendation is to rehearse the entire sign-in route before the first live shift. Start at the actual workstation, use the enrolled phone, complete the handoff, and sign out according to workplace procedure. This exposes configuration problems while support is available instead of during a patient-facing task.
Second, keep the phone’s role personal and deliberate. Do not hand it to a colleague to approve a request on your behalf, even if the intention is simply to save time. The point of the workflow is to connect access with the correct user. A shortcut at this stage weakens the very separation the app is meant to support.
Third, treat phone changes as an access event. If the device is replaced, lost, or reset, contact the organization’s approved support team before assuming the existing setup will transfer normally. This habit prevents a common mistake: discovering that the authentication device is no longer recognized only when urgent access is needed.
Finally, distinguish an app failure from an account or workstation failure. If the phone opens but the computer does not continue, the issue may be elsewhere in the chain. Recording where the process stopped gives support staff something more useful than simply saying that “the app does not work.” That small change in reporting can shorten troubleshooting.
My overall assessment
Imprivata ID is a specialized medical authentication app with a clear purpose: helping clinical professionals complete a secure identity check as they access workplace systems. I like the way it fits into a shared-workstation scenario, especially when a clinician needs to move from computer to phone and back without passing credentials to another person.
Its main limitation is also its defining characteristic. This is not an independent utility whose value can be judged entirely from a personal installation. The experience depends on enrollment, employer configuration, phone availability, workstation behavior, and a sensible support process. That can make the first use feel less immediate than a consumer authentication app.
For the right user, I would recommend it because the workflow is focused and relevant to healthcare access. For everyone else, I would choose a broader authentication tool or password manager instead. The best reason to use Imprivata ID is not that it is free or widely installed; it is that an organization has built it into a clinical sign-in process and trained staff to use the handoff correctly.
My bottom line: use it when your medical workplace requires or supports it, test the full route before relying on it, and keep a clear recovery plan for phone or workstation problems. In that setting, it can turn a vulnerable shared-computer login into a more controlled routine. Outside that setting, its specialized design offers little advantage.
Gallery
Imprivata ID Pros and Cons
- Fast
- secure authentication for supported apps and services.
- Push approvals reduce the need to enter one-time codes.
- Works with biometric unlock on compatible devices.
- Can support passwordless access and stronger login policies.
- Useful for organizations managing employee identity securely.
- Requires an organization account and administrator setup.
- Limited usefulness for personal users without Imprivata services.
- Push notifications may fail with poor internet connectivity.
- Changing phones can require account re-enrollment.
- Some features depend on employer policies and supported systems.
Imprivata ID Frequently Asked Questions
What is Imprivata ID used for?
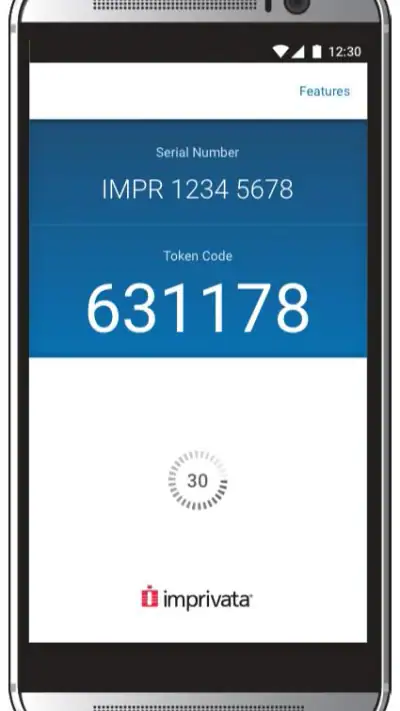
Imprivata ID is a mobile authentication application designed to help users securely verify their identity when accessing protected systems, applications, or services. It is commonly used in organizations that require multi-factor authentication. After enrollment, the app can provide approval prompts or security codes, depending on the configuration chosen by the organization and the identity platform being used.
How do I set up Imprivata ID on my Android or iPhone?
To set up Imprivata ID, you generally need an enrollment link, QR code, or activation instructions supplied by your employer, school, healthcare provider, or system administrator. Install the official app, open it, and follow the registration steps. You may need to allow notifications and enable device security features. Without valid enrollment information, the app cannot normally be used independently.
Does Imprivata ID require an internet connection?
An internet or mobile data connection may be required for certain authentication methods, especially when the app receives an approval request from an authentication server. However, some configurations may support generating a one-time passcode without continuous connectivity. Availability depends on how your organization has configured Imprivata’s authentication service, so users should confirm the required connection and backup options with their administrator.
Is Imprivata ID safe to use for account authentication?
Imprivata ID is built to add an extra layer of protection beyond a username and password. It can use device registration, push notifications, passcodes, and other security controls configured by an organization. Nevertheless, users should keep their phone updated, protect it with a screen lock, avoid approving unexpected login requests, and report a lost or compromised device immediately to the responsible administrator.
What should I do if I lose my phone or Imprivata ID stops working?
If your phone is lost, replaced, reset, or no longer receives authentication requests, contact your organization’s IT or security support team as soon as possible. They can disable the old device, issue a new enrollment method, or provide an approved backup authentication option. Reinstalling the app alone may not restore access because the device usually needs to be registered again.














